AML/CFT Compliance Audit in Oman: GoAML Reporting, DNFBP Inspections & FSA / CBO Governance Guide (2026)
For years, many business owners in Muscat assumed that Anti-Money Laundering and Combating the Financing of Terrorism (AML/CFT) audits were strictly a concern for commercial banks regulated by the Central Bank of Oman (CBO) or insurance and brokerage houses overseen by the Financial Services Authority (FSA, formerly the Capital Market Authority).
In 2026, that assumption has led to surprise regulatory inspections, heavy administrative fines, and commercial license suspensions across non-financial businesses throughout the Sultanate. Under *Royal Decree 30/2016 (Law on Combating Money Laundering and Terrorism Financing) and strict ministerial supervisory directives issued by the Ministry of Commerce, Industry and Investment Promotion (MOCIIP), the Ministry of Justice and Legal Affairs, and the National Centre for Financial Information (NCFI), thousands of Omani enterprises classified as Designated Non-Financial Businesses and Professions (DNFBPs)* are legally required to maintain an audited AML/CFT compliance program.
Whether you operate a real estate brokerage in Al Mouj or Qurum, a gold and precious metals bullion dealership in Muttrah Souq, a high-value motor vehicle showroom in Wattayah, a corporate service provider (CSP), or a financial institution in Ruwi’s Central Business District, regulators now expect four concrete pillars during an inspection:
- A written, entity-specific Enterprise-Wide AML/CFT Risk Assessment (
EWRA) and AML Compliance Manual; - Appointing and registering a qualified Money Laundering Reporting Officer (
MLRO/ Compliance Officer) on the NCFIGoAMLElectronic Portal; - Documented Customer Due Diligence (
CDD), Enhanced Due Diligence (EDD), and Ultimate Beneficial Ownership (UBO) verification files; and - An Independent AML/CFT Audit Report conducted by an external audit firm testing the effectiveness of your internal controls.
At Muscat Auditing & Accounting Services, our Enterprise Risk Management (ERM) & Internal Audit Practice in Oman conducts independent AML/CFT audits and regulatory remediation reviews for financial institutions, DNFBPs, and corporate groups across the Sultanate. Here is your complete 2026 compliance blueprint.
1. Which Omani Businesses Fall Under Mandatory AML/CFT Supervision & Independent Audits?
Following Oman’s rigorous alignment with the Financial Action Task Force (FATF) 40 Recommendations and MENAFATF mutual evaluation standards, supervisory authorities in the Sultanate divide regulated entities into two primary groups: Financial Institutions (FIs) and Designated Non-Financial Businesses and Professions (DNFBPs).
Here is the 2026 supervisory matrix showing which Omani regulator inspects your industry and what triggers mandatory AML audit scrutiny:
| Regulated Sector in Oman | Primary Supervisory Authority | Key Statutory Trigger & Inspection Focus |
|---|---|---|
| 1. Commercial Banks, Islamic Banks, Finance & Leasing Companies, Money Exchange Houses & PSPs | Central Bank of Oman (CBO) |
Mandatory annual independent AML/CFT audit, automated transaction monitoring, SWIFT wire screening, and real-time NCFI GoAML integration. |
| 2. Insurance Companies, Takaful Operators, Brokerage Firms, Investment Funds & Crowdfunding Platforms | Financial Services Authority (FSA — Royal Decree 20/2024) |
Annual external AML audit submission to FSA, politically exposed person (PEP) screening, and source-of-wealth verification on investment policies. |
| 3. Real Estate Brokers, Developers & Property Management Agencies | MOCIIP & Ministry of Housing and Urban Planning | Mandatory CDD/UBO verification on property buyers and sellers (especially cash, offshore corporate, or third-party wire purchases in ITCs and commercial plots). |
4. Dealers in Precious Metals & Gemstones (Gold, Bullion, Diamonds & Jewelry Traders) |
MOCIIP (Department of AML Supervision) | Mandatory customer identification, cash transaction threshold reporting (OMR 5,000+ / USD 15,000 equivalent), and bullion supply-chain due diligence. |
5. High-Value Goods & Luxury Motor Vehicle Dealerships (Auto Showrooms, Yachts, Luxury Assets) |
MOCIIP | Scrutiny of high-value cash deposits, third-party payer bank transfers, and structured installment payments. |
6. Corporate Service Providers (CSPs), Trust Services, Accounting & Audit Firms, and Legal Practitioners |
MOCIIP & Ministry of Justice and Legal Affairs | Mandatory KYB (Know Your Business), verification of Ultimate Beneficial Owners (UBOs), and screening of foreign company formation clients. |
2. The 6 Core Pillars Tested During an Independent AML/CFT Audit in Oman
When MOCIIP, the FSA, or the CBO requests your company’s Independent AML/CFT Audit Report—or when a correspondent bank asks for your AML assurance letter before opening a multi-currency corporate account—our Internal Audit & Risk Advisory Specialists evaluate your organization across six statutory pillars under Royal Decree 30/2016:
Pillar 1: Enterprise-Wide AML/CFT Risk Assessment (EWRA) & Risk-Based Approach (RBA)
Regulators immediately reject “copy-paste” AML manuals downloaded from the internet that reference foreign laws instead of Omani Royal Decrees. Your company must maintain a documented Enterprise-Wide Risk Assessment (EWRA) that scores inherent risk and residual control effectiveness across four dimensions:
- Customer Risk: Resident Omani individuals vs. non-resident foreign investors, Politically Exposed Persons (
PEPs), cash-intensive businesses, or complex offshore holding structures (BVI, Cayman, Panama). - Geographic Risk: Transactions involving jurisdictions listed on the FATF Grey List (Increased Monitoring) or FATF Black List (High-Risk Jurisdictions), or countries subject to UN Security Council / Omani National Terrorism List targeted financial sanctions.
- Product / Service Risk: High-value off-plan real estate purchases, physical gold bullion trades, or cross-border trade finance.
- Delivery Channel Risk: Non-face-to-face digital onboarding or payments remitted by unrelated third parties.
Pillar 2: Customer Due Diligence (CDD), Enhanced Due Diligence (EDD) & UBO Verification
Every client file sampled during our AML audit must contain verifiable Know-Your-Customer (KYC) and Know-Your-Business (KYB) documentation obtained before executing the transaction:
- For Individual Clients: Valid Omani Civil ID (
Resident Card) or Passport, proof of residential address, occupation, and documented purpose of the transaction. - For Corporate Clients (
KYB): Commercial Registration (CR) extract from the Oman Business Platform, Chamber of Commerce (OCCI) certificate, Authorized Signatory specimen, Articles of Association, and—crucially—the official Ultimate Beneficial Owner (UBO) Declaration identifying every natural person who ultimately owns or controls 25% or more of the shares or voting rights (aligned with Ultimate Beneficial Ownership (UBO) Compliance on the Oman Business Platform). - When
EDDIs Mandatory: Whenever a client is flagged as a Politically Exposed Person (PEP), a family member or close associate of a PEP, or originates from a high-risk jurisdiction, your team must execute Enhanced Due Diligence (EDD): obtaining written Senior Management approval, verifying Source of Wealth (SoW) and Source of Funds (SoF) via audited financial statements or bank statements, and conducting intensified ongoing transaction monitoring.
Pillar 3: Targeted Financial Sanctions (TFS) Screening Against UNSCR & Omani National Lists
Under decisions of Oman’s National Committee for Combating Terrorism and United Nations Security Council Resolutions (UNSCR 1267, 1373, and proliferation financing resolutions), every Omani entity (both FIs and DNFBPs) has a strict, zero-tolerance legal obligation to screen customers, UBOs, directors, and payment counterparties against:
- The UN Security Council Consolidated Sanctions List; and
- The Sultanate of Oman Domestic Terrorism & Sanctions List.
If a true positive match is identified, the entity must immediately and without prior notice freeze the funds/assets within 24 hours, prohibit any transaction, and report the freeze immediately via the NCFI GoAML system and to the relevant supervisory authority.
3. NCFI GoAML Registration & Suspicious Transaction Reporting (STR) Protocol in Oman
The National Centre for Financial Information (NCFI) is Oman’s Financial Intelligence Unit (FIU), headquartered in Muscat. Every regulated financial institution and DNFBP in Oman must register its organization and its designated Money Laundering Reporting Officer (MLRO) on the NCFI’s electronic GoAML platform.
During a regulatory inspection by MOCIIP or the FSA, inspectors immediately ask for two proofs:
- Your active
GoAMLRegistration Confirmation showing the registered MLRO’s credentials; and - Your internal Unusual / Suspicious Transaction Escalation Log (even if zero external STRs were ultimately filed with the NCFI during the year!).
Red-Flag Indicators That Must Trigger an Internal MLRO Review in Oman:
- Structuring (
Smurfing): A buyer attempting to split a OMR 25,000 payment for gold bullion, a luxury SUV, or a real estate plot into five separate OMR 5,000 cash deposits across consecutive days to evade cash reporting thresholds. - Unrelated Third-Party Wire Transfers: A client purchasing a commercial warehouse in Ghala or a villa in Muscat where the bank transfer arrives from an unrelated trading company in a third jurisdiction with no commercial connection to the buyer.
- Sudden Refund Requests After Cash/Foreign Wire Deposit: A customer pays a large advance deposit for an off-plan property or heavy equipment order and shortly thereafter cancels the contract, asking for the refund to be wired to a different bank account or third party.
- Refusal to Disclose UBOs: A corporate buyer refusing to provide passport copies or shareholding proof for the natural persons standing behind an offshore holding company.
Strict Anti-Tipping-Off Law (Royal Decree 30/2016): Under Omani criminal law, it is a serious offense (punishable by imprisonment and heavy fines) for any director, accountant, salesperson, or MLRO to “tip off” (warn or disclose to) a customer or any third party that a Suspicious Transaction Report (
STR) or information request is being filed with the NCFI.
4. What Happens During an Independent AML/CFT Audit by Muscat Auditing & Accounting Services?
Under Royal Decree 30/2016 and supervisory circulars from the CBO, FSA, and MOCIIP, the Independent AML/CFT Audit Function must be completely independent of the compliance officer (MLRO) and front-line business units. Your own MLRO cannot “audit themselves.”
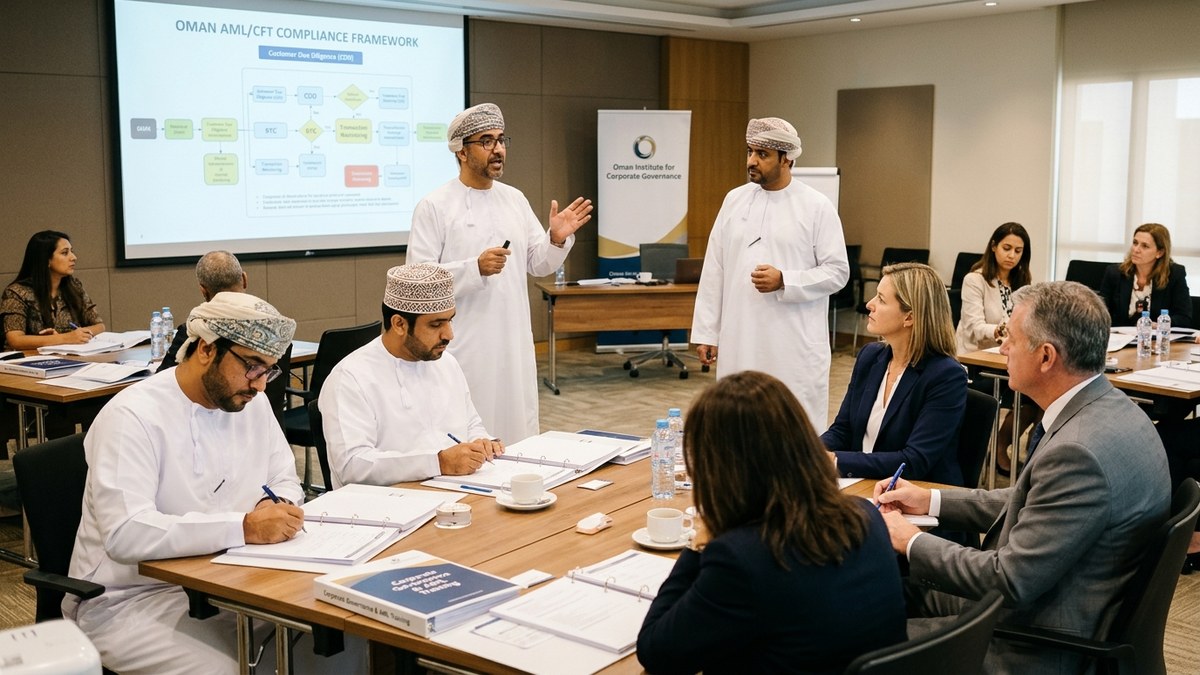
When you engage our Regulatory & Compliance Services Team in Oman (as demonstrated in our Internal Controls Enhancement Case Study for a Leading Omani Firm), we execute a structured 5-phase assurance engagement:
- Phase 1 — Policy & EWRA Gap Analysis: We benchmark your AML/CFT Policy Manual, Customer Acceptance Policy, and Enterprise-Wide Risk Assessment against Royal Decree 30/2016 and the latest 2025–2026 MOCIIP/FSA/CBO supervisory circulars.
- Phase 2 — Sample File Testing (
CDD,EDD&UBOFiles): We select a statistically representative sample of high-risk, medium-risk, and low-risk customer onboarding files, testing whether Civil IDs/CRs, UBO forms, source-of-funds proofs, and Senior Management EDD approvals are properly documented. - Phase 3 — Sanctions Screening &
GoAMLTechnical Testing: We test your sanctions screening software/process using dummy test profiles (UNSCR & Oman National List names) to verify that fuzzy-name matching and 24-hour freeze workflows operate without gaps. - Phase 4 — 10-Year Record Retention & Training Verification: Under Omani AML law, all CDD files, transaction records, and STR logs must be retained for at least 10 years from the date of transaction completion or account closure. We also verify attendance logs, test scores, and training materials for your mandatory Annual Staff AML/CFT Training.
- Phase 5 — Formal Independent Audit Report & Board Remediation Plan: We issue a signed Independent AML/CFT Audit Report with time-bound corrective action recommendations ready for presentation to your Board Audit Committee and submission to MOCIIP, the FSA, or the CBO.
5. Penalties for AML/CFT Non-Compliance Under Royal Decree 30/2016
Why are Omani boards prioritizing AML compliance in 2026? Because administrative and criminal sanctions under Royal Decree 30/2016 are severe:
- Administrative Supervisory Sanctions: Regulatory authorities (CBO, FSA, MOCIIP) can impose written warnings, hefty administrative fines per violation, removal or disqualification of the MLRO or General Manager, restriction of commercial activities, or suspension/revocation of the Commercial Registration (
CR) or professional license. - Corporate Criminal Fines: Corporate legal persons convicted of money laundering offenses face fines ranging from OMR 100,000 up to the full value of the laundered funds, alongside confiscation of proceeds and judicial dissolution of the entity.
- Commercial Banking De-Risking: Even before a government fine hits, if your company fails its annual KYB/AML review with Bank Muscat, Bank Dhofar, or Sohar International, the bank’s compliance unit can restrict cross-border SWIFT transfers or close your corporate accounts.
6. Related Omani Compliance & Audit Guides
Explore the rest of our 2026 corporate compliance series for Omani businesses:
- Social Protection Fund (SPF) Oman & End-of-Service Gratuity Audit Guide (Royal Decree 52/2023 & 60/2025)
- Oman Tax Authority (OTA) Audit Defense, Tax Card Renewal & 15% Corporate Tax Guide
- Construction, Real Estate & EPC Contracting Accounting, IFRS 15 & VAT Audit in Oman
- MOCIIP Audited Financial Statements Filing, CR Renewal & AGM Compliance on Oman Business Platform
7. Frequently Asked Questions (FAQs): AML/CFT Audits & DNFBP Compliance in Oman
1. What is a DNFBP in Oman, and do DNFBPs need an AML/CFT compliance program?
DNFBP stands for Designated Non-Financial Businesses and Professions. Under Oman’s AML/CFT Law (Royal Decree 30/2016), DNFBPs include real estate brokers and developers, dealers in precious metals and gemstones (gold and jewelry traders), corporate service providers, lawyers, and accountants/auditors. Every DNFBP in Oman is legally required to register on the NCFI GoAML portal, appoint a Compliance Officer (MLRO), perform Customer Due Diligence (CDD), and undergo independent AML compliance audits.
2. How long must Omani companies retain KYC, CDD, and AML transaction records?
Under Royal Decree 30/2016, all financial institutions and DNFBPs in Oman must retain Customer Due Diligence (CDD) documents, Ultimate Beneficial Owner (UBO) declarations, transaction files, and internal/external AML correspondence for a minimum of 10 years following the completion of the transaction or the termination of the business relationship.
3. What is the GoAML system in the Sultanate of Oman?
GoAML is the secure electronic reporting platform operated by Oman’s National Centre for Financial Information (NCFI)—the national Financial Intelligence Unit (FIU). All regulated financial institutions and DNFBPs in Oman must register their Money Laundering Reporting Officer (MLRO) on GoAML to submit Suspicious Transaction Reports (STRs), cash threshold reports, and targeted financial sanctions freeze notifications.
4. What is the ownership threshold for identifying an Ultimate Beneficial Owner (UBO) in Oman?
Under MOCIIP’s Ultimate Beneficial Ownership regulations and AML/CFT guidelines in Oman, an Ultimate Beneficial Owner (UBO) is any natural person who ultimately owns or controls—directly or indirectly through a chain of corporate entities—25% or more of a company’s shares or voting rights, or who exercises ultimate effective control over the company’s management.
5. Can our company’s internal Compliance Officer (MLRO) sign our annual AML/CFT Audit Report?
No. Under Omani regulatory standards (CBO, FSA, and MOCIIP AML directives), the independent AML/CFT audit must be performed by an audit function or external audit firm that is operationally independent from the MLRO and the compliance department responsible for day-to-day onboarding and transaction monitoring.
Need an Independent AML/CFT Audit or DNFBP Compliance Setup in Oman?
Protect your commercial license and banking relationships. Muscat Auditing & Accounting Services delivers independent AML/CFT assurance reports, custom Enterprise-Wide Risk Assessments (EWRA), GoAML onboarding, and staff training tailored to MOCIIP, FSA, and CBO standards.
Request an AML Audit Proposal or explore our Enterprise Risk Management & Internal Audit and Regulatory Compliance Services.